Google warns visitors about your website, visitors end up on unknown sites, or the hosting provider has suspended the account? We isolate the website, close the vulnerability and clean the website within 24 hours of access, weekends included. Afterwards you receive a written report.
Taking over, updating and securing WordPress websites
Your website or online shop runs on WordPress, and nobody looks after updates, plugins and security any more? We take over the support, test updates on a staging copy first, clear out abandoned plugins and secure the website.
- PHP and WordPress since 2012
- Updates tested on a staging copy
- Support and emergencies around the clock
Where we use WordPress
Our engineers have worked with WordPress since 2012, as part of their work with PHP. We look after websites, portals and WooCommerce shops, with purchased and custom plugins and with interfaces to other systems.
Often an agency or a single developer built the website, and today nobody feels responsible for it. We take over the support, catch up on updates and make sure your website stays secure and available. The foundation is PHP; more on that under PHP & Craft CMS.

Typical tasks with WordPress
- Takeover: securing access to hosting, domain, admin area and database, and recording plugins and themes.
- Updates of WordPress, themes and plugins, with a backup beforehand and a test on a staging copy.
- Cleaning up plugins: replacing or removing abandoned and duplicate plugins.
- WooCommerce: updates of the shop and its extensions, with a test of the checkout.
- Adjustments to theme and plugins, interfaces to a CRM, an ERP system or a newsletter service.
- Update to a supported PHP version; see PHP 8 upgrade.
- Backups with a regular restore test.
- Faster load times: caching, slow database queries and oversized images.

Updates tested before they reach production
A plugin update can break a form, the shopping cart or the layout. That is why we apply larger updates first to a copy of your website with current data. There we check the most important processes: forms, login and, for a shop, the order through to the confirmation.
Only then do we update production, in an agreed time window and with a backup beforehand. If something does not work as expected, we return to the state before the update. Urgent security updates do not wait for the next window.

Securing WordPress
- Access to the admin area: two-factor login, and only the user accounts and permissions that are needed.
- File permissions set so that the admin area cannot change any code.
- Plugins only from maintained sources; abandoned plugins are removed.
- A WAF on the server with rules that fit your website.
- Backups outside the server, and monitoring of availability and errors.
More on securing websites and applications under Web application and website security.

If your website has been hacked
Google warns about your website, visitors are redirected to pages that are not yours, or the hosting provider has blocked the site? Then a fast and orderly procedure helps more than a hasty restore. What we do in the first hours, and what you should rather not do until then, is described under Website hacked?. Support and emergencies are available around the clock.

Technologies and scope
| Area | Scope |
|---|---|
| CMS | WordPress since 2012, also with WooCommerce |
| Language | PHP for themes, plugins and interfaces |
| Databases | MySQL and MariaDB |
| Operations | Linux and Docker |
| Web servers and protection | Nginx and Apache, a WAF with rules tuned to the website |
Typical starting points with WordPress
-
-
Security updates for PHP 8.2 end on 31 December 2026, and for PHP 8.1 and older they have already ended (As of 2026-10). We move long-running PHP applications, including those with Smarty templates and jQuery front ends, to PHP 8.4 or 8.5 and test every stage.
The first step: a CMS check
CMS check: WordPress and Craft CMS
For companies with a business-critical WordPress or Craft CMS website and no agency or maintainer any more: before a takeover, before a major update or after a security incident.
- Versions of CMS, PHP, database and server, and their support status
- Plugins and themes: what is maintained, what is abandoned and what should be replaced
- Updates: what is missing and how risky it is to catch up
- Backups: what is backed up and whether a restore has been tested
- Security: admin access, two-factor login, user permissions and known vulnerabilities
- Licences for the CMS and commercial plugins: which ones exist and in whose name they are registered
At this stage we change nothing on the website. We check custom themes and plugins for maintenance status and known vulnerabilities, not line by line. The check covers one website; we price further websites individually.
What the result contains
A written report with the risks in order of priority and a plan for takeover, updates and ongoing support. The report is yours.
Typically 2 working days
Request a CMS checkA project with WooCommerce
-
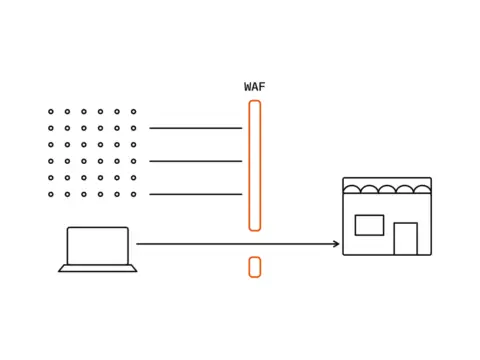
A shop flooded by bots that looked like customers
A WooCommerce shop with 52 products loaded slowly or not at all. The cause was a paid network of bots sending tens of thousands of requests an hour, each from a different home address, and every single bot behaved perfectly. Our engineers stopped the traffic at the edge of the network, and when the bots changed tactics a month later, the second rule took the load off within two minutes.

Questions about WordPress
Are the automatic updates in WordPress not enough?
They are a good foundation, but they do not cover everything. A larger update of a plugin, the theme or WooCommerce can break forms, the layout or the checkout. An abandoned plugin no longer gets any updates, not even for a known vulnerability.
That is why we make a backup before every larger update, test it on a staging copy first and then check the most important processes. We replace or remove abandoned plugins.
Do you also look after WooCommerce shops?
Yes. For a shop, we check the path from the cart to the order confirmation after every larger update. We do this on a staging copy first and then in production. Payment and shipping plugins and interfaces to ERP or accounting systems are part of this test.
We apply updates at times with few orders, with a backup beforehand.
Can you take over our website if the agency no longer works with us?
Yes. What matters is access to the hosting or server, the domain and the admin area. If there is no repository, we take the code and the database from the server and create a new repository that belongs to you.
In the CMS check we record what is installed, which plugins and licences exist and what is missing. If the agency helps with the handover, things go faster.
What if we are missing access credentials?
This can usually be solved. We start with what you still have to hand. That is the contract and customer account with the hosting provider, access to the domain and, where available, the repository and backups. Server access can often be reset through the hosting provider if you act as the contracting party. We only gain access to a system with your explicit consent.
Do you cover weekend duty from time to time?
Yes. Support and emergencies are covered around the clock (24/7), weekends included. For other enquiries we are available Monday to Friday, 9:00 to 17:00 Central European Time, and we reply within one working day.
Not sure which service fits your system?
Describe your system in two sentences. We will tell you which service fits and whether an entry product at a fixed price is the right first step.